
We have identified that unsolicited emails from Carelogix have been circulating. As a precaution, we have taken immediate action to secure the account, including:
Locking down the affected account to prevent further unauthorised use
Force re-authorisation on all devices
Resetting the account password
Confirming that multi-factor authentication (MFA) remains active and enforced on this account
Because MFA was already in place, we assess the potential impact and exposure to be limited. We have found no evidence at this stage that any client data or internal systems have been compromised, and we are continuing to monitor the situation closely.
What we recommend if you have received an email from this address recently:
Do not click links or open attachments unless you can verify the sender
Do not action any request for payment, credentials, with us by phone
If in doubt, contact us directly using the details on our official website
We take the security of our communications seriously and are reviewing our processes to further reduce the risk of similar incidents in the future. We will provide a further update if our investigation identifies any additional impact.
If you have any concerns or have received a suspicious email you'd like us to review, please contact us on our website directly.
Thank you for your understanding.
— The Carelogix Team
Further Updates at 10:30 PM
We received a great number of support through LinkedIn and below were further actions taken.
Impact Assessment - it was identified that approximately 1000 users were affected by the recent phishing attack and it is isolated to our email communication system.
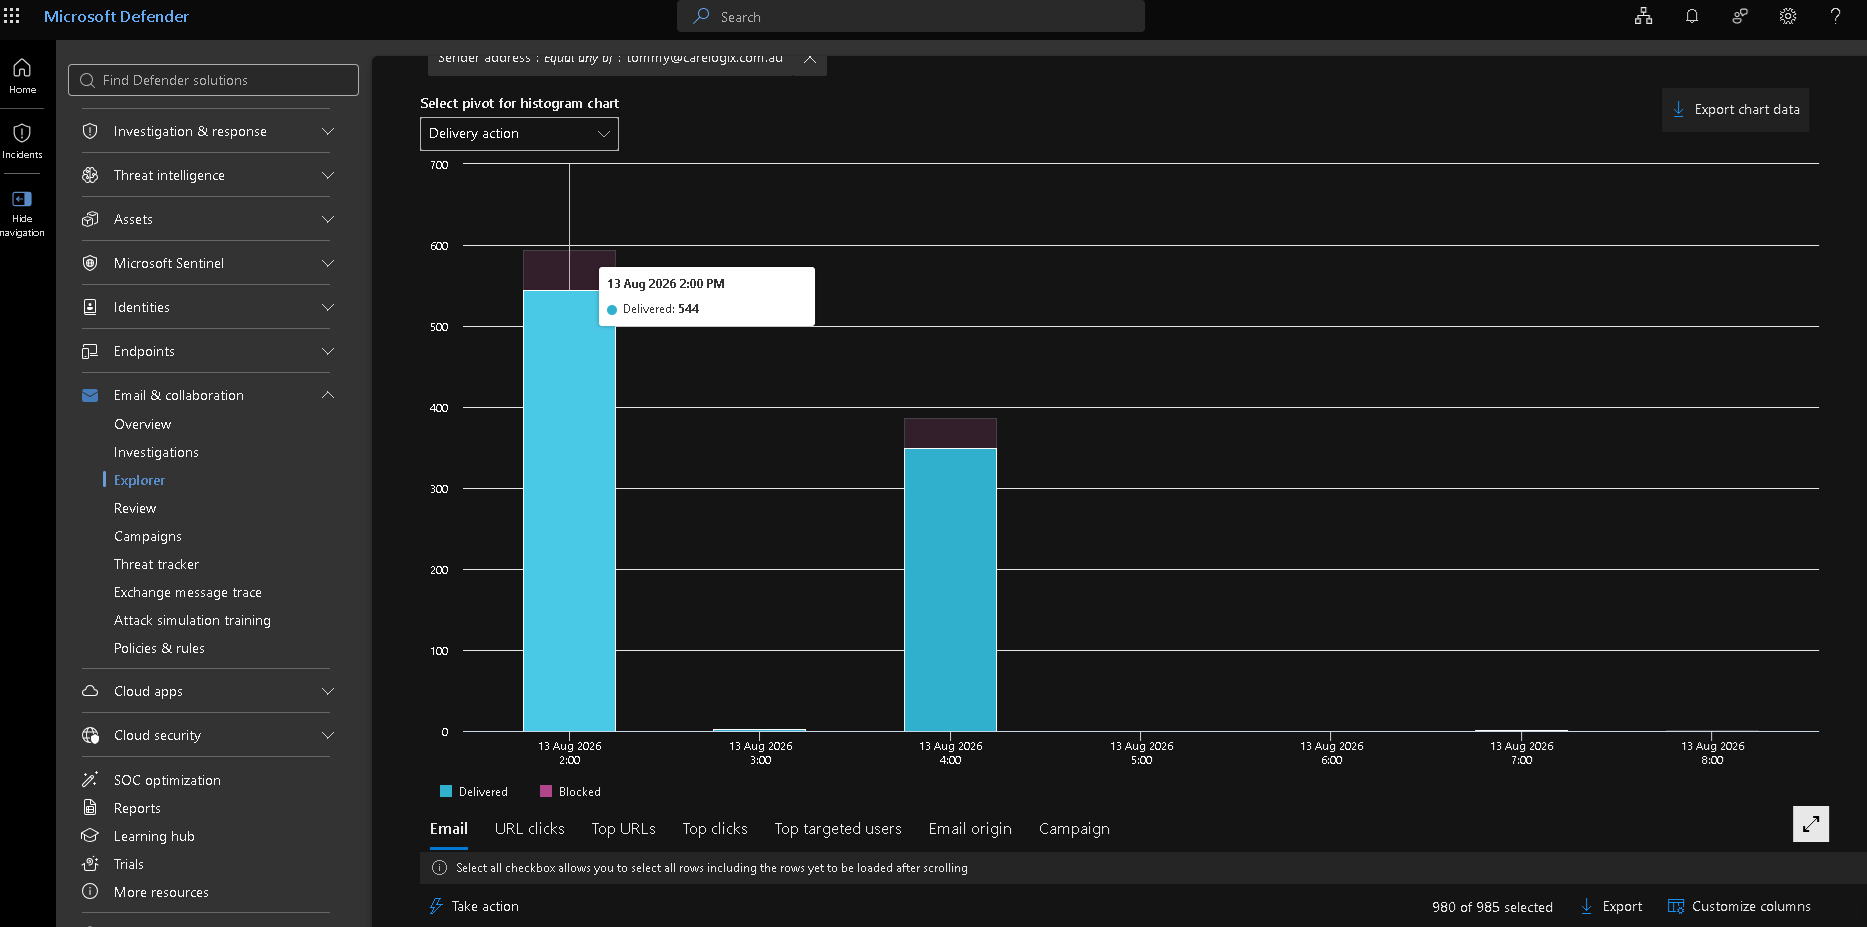
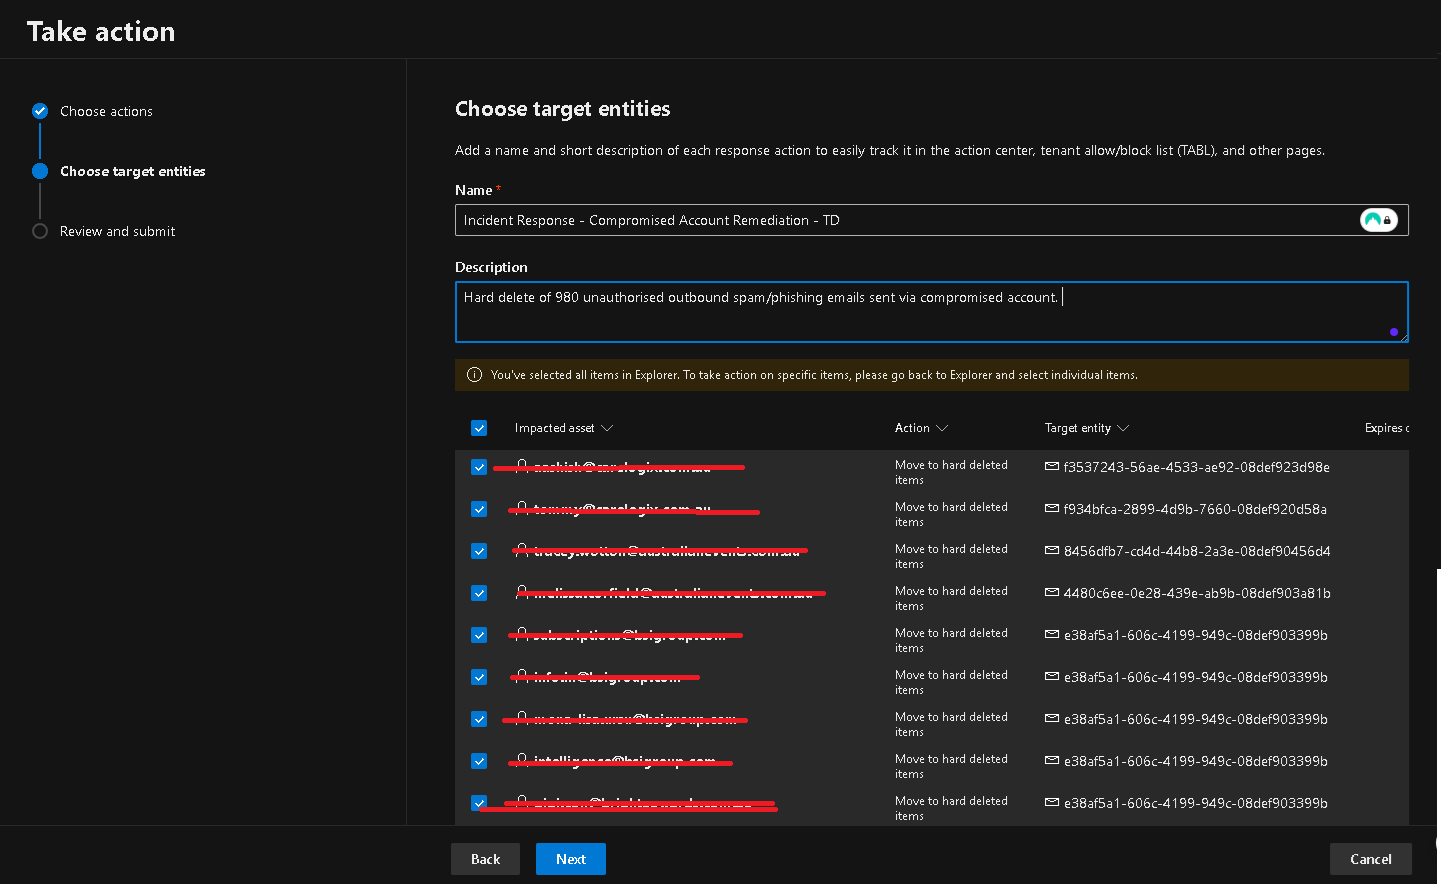
Incident response - delete the unauthorised outbound phishing messages sent via compromised account.
To strengthen our existing security, we adopted two new policies, first policy, everyone requires MFA to enter the system followed by second policy, that is tied to relevant Geolocations.
Kind regards,
Tommy Dam
Related Articles

Australia Healthcare Week 2040 EXPO Mar 2026
Australian Healthcare Week 2040 at the Sydney ICC was a convergence of clinicians, operators, builders, and investors, all circling the same stubborn problem from different angles

Sydney Emergence Feb 2026
The Sydney Emergence 2026 conference spanned three intensive days, bringing together a powerhouse lineup of founders, institutional investors, and family offices.

Live on Apple App Store Jan 2026
Introducing Carelogix Note – Where Care Meets Intelligence